ABOUT
About My Databoss
ABOUT
About My Databoss
My Databoss - Privacy policy
Version : 2
Last updated: 25th September 2026
My Databoss Pty Ltd (ABN 92 670 573 270) (MDB, we, us, our) is committed to protecting the personal information we collect, including through our Platform, Website and other tools. This Privacy Policy explains how we collect, hold, use and disclose personal information in accordance with the Privacy Act 1988 (Cth) (Privacy Act) and the Australian Privacy Principles (APPs).
This Policy is in three parts. Part 1 applies to individuals whose identity or business is verified through the Platform. Part 2 applies to our clients, prospective clients, website visitors and other business contacts. Part 3 applies to everyone.
Part 1 – Individuals Verified Through Our Platform
Our clients, including real estate agencies, legal practices and accounting practices regulated under the Anti-Money Laundering and Counter-Terrorism Financing Act 2006 (Cth) and associated Rules (AML/CTF Act), engage us to run identity (KYC), business (KYB) and AML/CTF screening checks on their customers, vendors and employees. If you are completing a check at a client's request, we handle your personal information on that client's instruction to support its regulatory obligations. The client remains your point of contact for why a check is required and what happens if it is not completed. If you use our App or Platform directly, you will also accept our End User Licence Agreement (EULA), which governs your use of the App or Platform alongside this Policy.
Information we collect
- Identity Data: name, age, date of birth, gender, profession and photographic identification.
- Verification Data: government-issued identification details and document images (which may draw on the 100-point identification system), proof of address, and biometric information (a selfie image and liveness-check video matched to your identification document).
- Business Verification Data: ABN/ACN, business structure, officeholder and beneficial ownership information, where a check relates to a business.
- Bank Account Data, where requested by our client in the course of providing services to you.
- Contact Data: telephone number, address and email.
- Technical and Usage Data generated while you complete a check, such as IP address, device and session data. Our App may request access to your device's camera, microphone, GPS location and biometric authentication (such as Face ID or Touch ID) where you grant those permissions.
How we use and disclose it
We use this information to perform the check requested by our client and to help the client meet its customer due diligence, enhanced due diligence and ongoing monitoring obligations under the AML/CTF Act. We may also create de-identified, aggregated statistics from verification information (for example, to understand trends across checks or improve the accuracy of the Platform) and use or publish those statistics for our own purposes, including product development. We do not use your identity or verification information for marketing, or for any purpose unrelated to verification, without your explicit consent.
To run a check, we disclose your information to:
- the client who requested the check;
- our accredited document verification provider under the Australian Government's Document Verification Service (DVS);
- our bank account verification provider, where bank account verification is requested;
- our identity verification provider, which processes document and biometric data;
- our business verification and credit bureau data provider, which processes business and officeholder data and verifies identity documents against government records;
- our AML/CTF screening provider, which screens against sanctions, politically exposed persons (PEP) and adverse media lists; and
- our IT hosting, storage and infrastructure providers.
We share biometric information with a third party only with your express consent, or where required or authorised by Australian law or a court or tribunal order.
Our clients warrant to us that they have obtained the consents and given the notifications required under the Privacy Act before providing your information to the Platform, and are contractually required to comply with the Privacy Act and protect the information they receive from us. Once a client receives your verification result, the client's own privacy policy governs its further handling of that information; this Policy does not extend to it. Questions about how your information came to be provided to us should be directed to the client.
We may also disclose your information to courts, tribunals, regulators (including AUSTRAC, where relevant to a client's obligations) and law enforcement, as required or authorised by law or in connection with legal proceedings.
Automated decision-making
The Platform uses computer programs supplied by our verification partners, including artificial intelligence, biometric matching and document authenticity checks, that use your personal information to produce verification outcomes. Consistent with Australian Privacy Principle 1.7:
- Personal information used: identification document details and images; biometric information (selfie image and liveness-check video); name, date of birth and address; business ownership and officeholder information for business checks; and bank account details where requested by the client.
- Decisions made solely by a computer program: whether your identification document matches the issuing authority's records (via the DVS); whether your selfie matches the document photograph and passes a liveness check; whether a document shows signs of alteration or fraud; whether your name matches a sanctions, PEP or adverse-media watchlist entry; and whether a business's registered details match ASIC records. These produce a result of Pass, Reject or Review Needed. Reject and Review Needed results are checked by a person before they are finalised.
- Decisions substantially informed by a computer program: the verification result and any risk rating are provided to the client as an input into the client's own decision, for example whether to onboard you or proceed with a transaction. That decision is made by the client, not MDB, and may be adverse or
If a check does not pass, you may ask the client to have it reviewed or contact us (Part 3). Alternative verification methods that do not rely on the DVS are available where an automated check cannot be completed.
Overseas disclosure
Some of our identity verification and other service providers are located overseas, including in the United States of America and the European Union. By using the Platform, you acknowledge that your personal information may be transferred to and stored in those countries. We take reasonable steps to ensure overseas recipients handle your personal information consistently with the APPs.
Retention and your rights
Biometric data collected during liveness verification is retained for up to 72 hours after your verification is completed, then securely deleted. Verification outcomes, audit logs and related records are retained for as long as needed to meet our clients' record-keeping obligations under the AML/CTF Act and our own legal obligations; the period depends on the client's compliance requirements. The Platform tracks retention and expiry and automatically deletes expired personal information.
The Platform's end-user controls let you manage who can view, request or share your personal information, and delete your information directly within the App. You may also request deletion by emailing support@mydataboss.com; we will action requests in accordance with applicable law.
Because verification records are held on behalf of the client, access and correction requests should go to the client first. You may also contact us (Part 3) and we will assist or redirect your request. Information used to complete a check may not be correctable once the check is finalised, as it must be retained to support that check.
Part 2 – Clients, Website Visitors and Other Business Contacts
This Part applies if you engage with MDB directly, for example as a representative of a client, a prospective client, a website visitor, a job applicant or another business contact, rather than as an individual being verified at a client's request (see Part 1).
Information we collect
- Contact Data: telephone number, address and email.
- Financial Data: bank account and payment card details, for billing.
- Profile Data: Platform username and password, profile picture, orders, content you post or share through the Platform, and support requests.
- Technical and Usage Data: IP address, login data, browser session and geo-location data, page views, device and network information, acquisition sources, search queries and browsing behaviour.
- Interaction Data provided through surveys, contests, promotions, activities or events.
- Marketing and Communications Data: your marketing and communication preferences.
- Professional Data, where you apply for a role with us: your professional history and experience.
How we collect it
- directly from you, whether in person, by phone, by email or online;
- when you complete a form, register for an event or newsletter, or respond to a survey;
- when you apply for a job with us;
- from analytics, cookie and marketing providers (see Cookies in Part 3); and
- from public sources such as social media and ASIC.
How we use and disclose it
We use this information to:
- provide you with access to and use of the Platform, including a login;
- assess whether to take you on as a client, including fraud and background checks;
- do business with you, including record keeping, administration, invoicing and billing;
- respond to support requests and enquiries;
- conduct analytics, market research and business development to operate and improve our business;
- run promotions and competitions and offer benefits;
- consider your employment application; and
- comply with our legal obligations.
Marketing and communications: you agree that we may send you electronic communications about our products and services, including software updates and changes to our terms. You may opt out at any time using the unsubscribe function in those communications.
We may disclose this information to:
- our employees, contractors and related entities;
- IT, data storage, web-hosting and server providers;
- our offshore staffing and support providers;
- marketing and advertising providers;
- professional advisers, bankers, auditors, insurers and insurance brokers;
- our payment processor;
- existing or potential agents and business partners;
- anyone to whom our business or assets (or any part) are, or may in good faith be, transferred; and
- courts, tribunals, regulators and law enforcement, as required or authorised by law, including to recover unpaid fees or in connection with legal proceedings.
Part 3 – General Provisions
Data retention
We retain personal information only as long as reasonably necessary for the purposes for which it was collected, having regard to our and our clients' legal, regulatory and accounting obligations (including AML/CTF Act record keeping), the need to respond to enquiries, disputes or complaints, and technical constraints such as backups. Biometric data from liveness verification is retained for up to 72 hours (see Part 1). Backup copies retained after deletion from live systems are kept secure and separate from further processing until removed in the ordinary backup cycle. When information is no longer required, we take reasonable steps to destroy or de-identify it. Unsolicited personal information that we could not lawfully have collected is destroyed or de-identified as soon as practicable, where lawful and reasonable.
Notifiable data breaches
We maintain processes to detect, respond to and manage data breaches. If a breach is likely to result in serious harm to any affected individual, we will comply with the Notifiable Data Breaches scheme in Part IIIC of the Privacy Act, including notifying the Office of the Australian Information Commissioner (OAIC). Where practicable we notify affected individuals directly; where we do not hold their contact details, we provide the relevant client with a statement to pass on.
Your rights
Choice: you need not provide personal information to us, but if you do not, we may be unable to do business with you, or our client may be unable to onboard you.
Information from third parties: personal information we receive from a third party, including a client, is protected as set out in this Policy. If you provide personal information about someone else, you warrant that you have their consent.
Unsubscribe: to opt out of marketing or other communications, use the unsubscribe facility provided or contact us.
Access and correction: you may request access to, or correction of, the personal information we hold about you. An administrative fee may apply to access requests. Where the law permits us to refuse a request, we will tell you why as soon as reasonably possible and how to complain, and will provide access in another form where that meets your needs.
Complaints: contact us with full details and we will investigate and respond in writing with the outcome and any steps we will take. If you are not satisfied, you may contact the OAIC on 1300 363 992 or at oaic.gov.au.
Security
We maintain physical, electronic and managerial safeguards to protect personal information from misuse, interference, loss and unauthorised access, modification or disclosure. No internet transmission is completely secure; information is transmitted to and from us at your own risk.
Cookies
Our website may use cookies, which are small text files stored in your browser that recognise you on return and support our retargeting advertising. Cookies alone do not identify you, but may be linked to personal information you provide. You can block cookies in your browser settings, though some parts of our website may then be unavailable.
Links to other websites
Our website may link to third-party websites. We do not control those websites and are not responsible for their handling of your personal information; this Policy does not apply to them.
Amendments
We may vary this Policy at any time by publishing the amended version on our website. Please check regularly.
Contact us
My Databoss Pty Ltd (ABN 92 670 573 270)
Suite 603, Level 6, 1 Elizabeth Plaza, North Sydney NSW 2060
Email: support@mydataboss.com
The cost of getting it wrong
In Australia, non-compliance penalties can reach $22 million per breach, plus daily penalties of around $18,000. AUSTRAC and FATF expect group-wide consistency and accountability. Recent enforcement actions – including CBA ($700M) and Westpac ($1.3B) – demonstrate the regulator's posture.
Type of Failure |
Financial Impact |
| Late or inaccurate reporting | $50K–$200K per breach |
| System weakness or ongoing failure | $1M–$30M+ potential penalties |
| Severe or systemic non-compliance | Business-threatening enforcement |
Figures based on current penalty-unit values.
In 2023–24, the cost of organised crime to Australia grew to $82.3 billion, a sharp $13.6 billion increase from $68.7 billion the previous year.*
Old way
Manual processes and fragmented tools
- Policy documents in a folder
- Identity stored in emails
- Risk in someone’s head
- Ad hoc monitoring
- Manual spreadsheet reports
- Training by word of mouth
New way
Integrated, end-to-end AML/CTF workflows
- Live compliance system
- Verified identity records
- Documented, scored risk ratings
- Ongoing alerts and reviews
- Logged, timestamped reports
- Recorded, trackable training
Meet My Data Boss
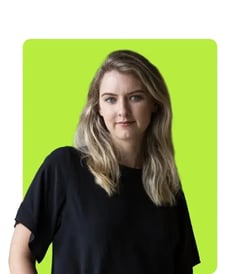
Greta Menzies
CEO
Greta is an AI and data governance expert with nearly two decades of experience delivering enterprise-scale transformation across finance, government and universities. With a strong track record in machine learning adoption and data strategy, she has led complex programs for major banks, retailers and institutions. At My Databoss, Greta has assembled a high-calibre team to execute on a bold vision: redefining secure data management for the AI era, with a platform built for scale, compliance, and global impact.
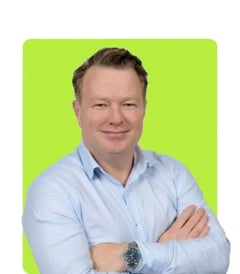
James Murphy
COO
James is a seasoned executive and operations leader with over two decades of experience across financial services, technology and data platforms. As a founding executive and CFO of a high-growth fintech that successfully scaled and exited to an ASX-listed company, he brings deep expertise in SaaS operations, cybersecurity, risk management and compliance. James plays a pivotal role at My Databoss, ensuring the business is built on strong operational foundations and ready to scale with integrity and confidence.
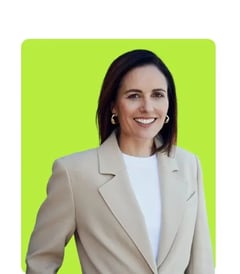
Kelly Ryan
CGO
Kelly RyanCGOKelly is a seasoned executive with over 20 years of experience leading major national organisations across the sports, entertainment and real estate sectors. Known for her strategic vision and commercial acumen, she has driven the growth and transformation of high-profile brands through innovation and modernisation. At My Databoss, Kelly leads market expansion and strategic partnerships, ensuring the business continues to deliver game-changing solutions that empower organisations globally.